Security at the Core.AI Without Exposure.
Move security from prompt suggestions into hardened database permissions, Kubernetes controls, and zero-trust CI/CD pipelines. We ensure even jailbroken LLMs cannot exceed their permissions.
Cloud Security & DevSecOps
Security First Approach
We implement Security-by-Design in every phase of your cloud migration and DevOps pipeline. Our experts seamlessly integrate security controls into your CI/CD processes.
OWASP Best Practices
Full compliance with OWASP standards, including Top 10 Web Application Security Risks, API Security and Cloud Security Guidelines.
Zero Trust Architecture
Implementation of Zero Trust principles for maximum security in multi-cloud and hybrid environments.
AI Security Leadership
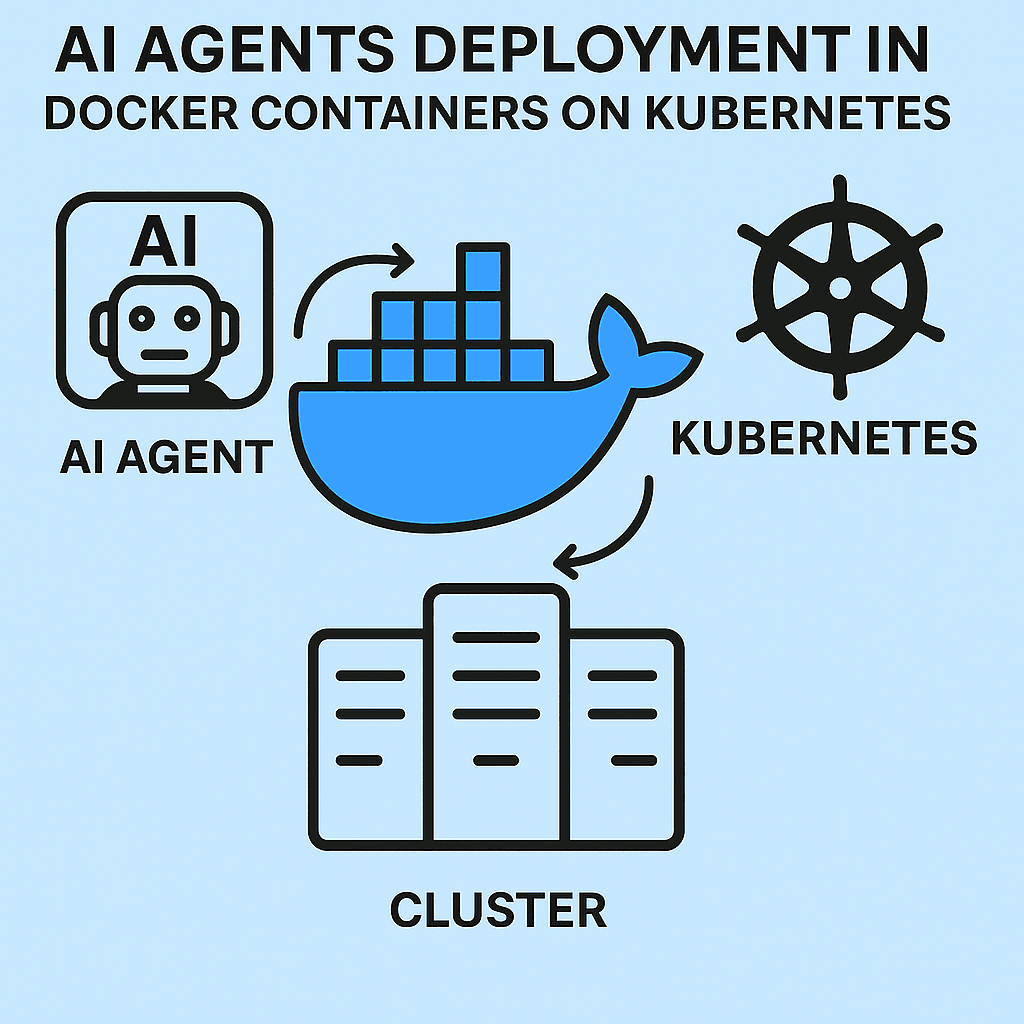
Secure AI Agents Deployment
Secure deployment and management of AI agents with robust authentication, authorization and monitoring mechanisms.
- Containerisierte AI Agent Isolation
- Encrypted Model Storage & Transfer
- Real-time Threat Detection
- Compliance-ready Audit Trails
Data Privacy & AI Ethics
GDPR-compliant AI implementations with Privacy-by-Design and ethical AI guidelines.
Secure MCP with ToolHive
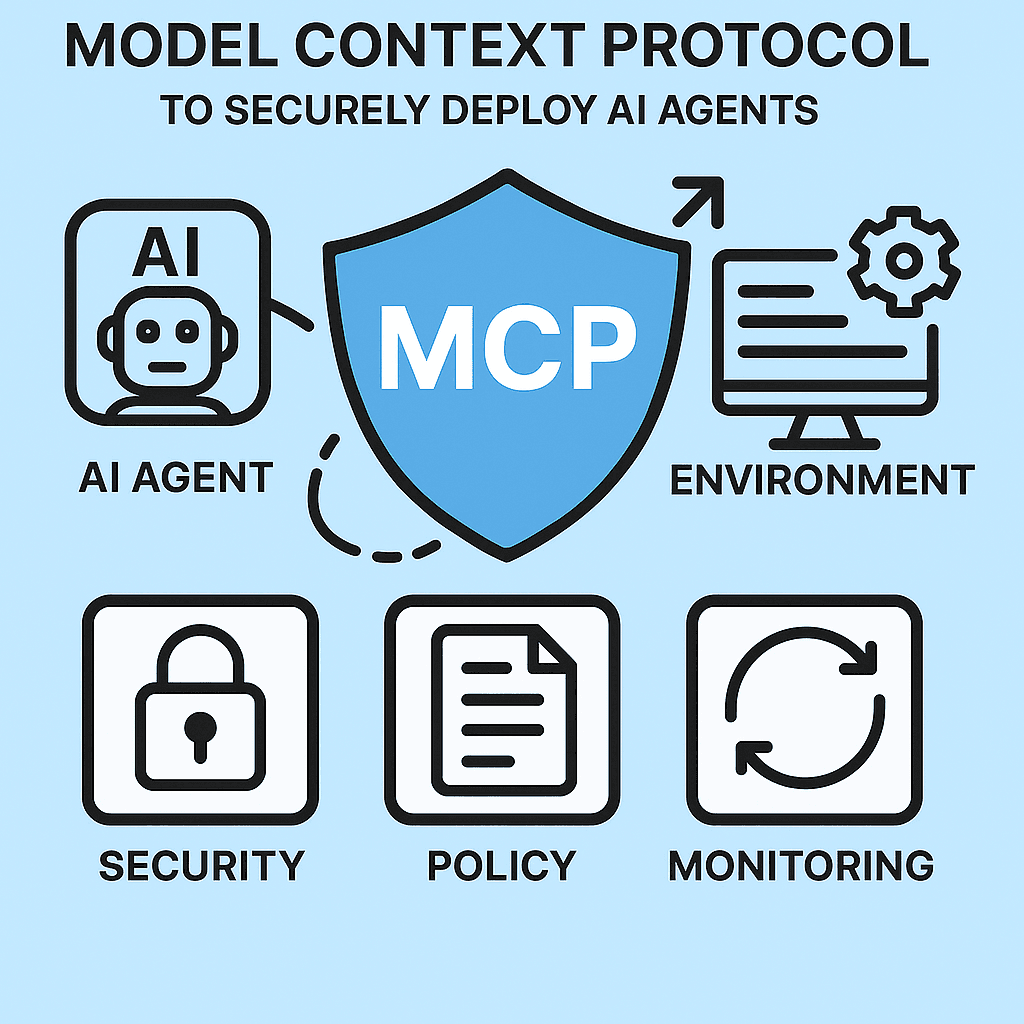
Enterprise-Ready MCP Security
As experts with tools like ToolHive, we implement secure Model Context Protocol (MCP) servers with:
- • Curated MCP Registry: Verified, secure MCP servers from trusted sources
- • Container Security: Minimale Permissions and locked-down environments
- • Secrets Management: Encrypted credential management without plaintext exposition
- • Enterprise Authorization: Robust access control for enterprise environments
ToolHive Key Benefits
- • Standardized Packaging: OCI Container Standards for consistency
- • Seamless Integration: Auto-configuration for GitHub Copilot, Cursor & more
- • Kubernetes-Ready: Enterprise deployment with our ToolHive Operator
- • Minimal Attack Surface: Security-by-default principles
Our Security Services
Security Architecture
Design and implementation of secure cloud architectures with Zero Trust principles.
Security Audits
Comprehensive security assessments and penetration testing for web apps and APIs.
DevSecOps Integration
Automated security testing in CI/CD pipelines with Infrastructure as Code.
Cloud Security
Multi-Cloud Security Management for AWS, Azure, Google Cloud and Kubernetes.
AI Security
Secure AI/ML pipelines, Model Protection and AI Ethics Compliance.
Compliance
GDPR, ISO 27001, SOC 2 and industry-specific compliance implementation.

FAQ about AI Security & DevSecOps
AI systems process sensitive data and make autonomous decisions. Security vulnerabilities can lead to data leaks, model manipulation, or unauthorized access. At TechChase, we implement Security-by-Design from the start in every AI deployment.
DevSecOps integrates security into every step of the DevOps process. Instead of treating security as an afterthought, we build automated security checks into CI/CD pipelines, perform continuous vulnerability scans, and implement Infrastructure Security as Code.
We implement Privacy-by-Design, encrypt data at-rest and in-transit, minimize data collection, enable deletion on request, and document all data processing. Our AI deployments meet GDPR and EU AI Act requirements.
Zero Trust means 'never trust, always verify'. Every request is authenticated and authorized, regardless of origin. We implement Zero Trust in Kubernetes with Network Policies, mTLS, Service Mesh, and granular RBAC roles for maximum security.
We use minimal base images, scan for vulnerabilities, implement Pod Security Standards, Network Policies, RBAC, Secrets Management with Vault, Image Signing, and Runtime Security Monitoring. Containers run with minimal privileges and read-only filesystems.
ToolHive is our curated, containerized MCP registry. Each MCP tool is security-audited, packaged in minimal containers, equipped with secrets management and RBAC controls. This massively reduces the attack surface.
We perform penetration testing, code security reviews, infrastructure security audits, OWASP Top 10 checks, container security scans, Kubernetes security assessments, and compliance audits (GDPR, ISO 27001).
We implement SIEM (Security Information and Event Management), Runtime Security Monitoring, anomaly detection, Intrusion Detection Systems (IDS), log aggregation, and alerting. Suspicious activities are detected and handled in real-time.